Yagami AI Context Firewall
LocalAbout Yagami AI Context Firewall
Yagami is an open-source context firewall for developers and platform or security teams governing how agent context reaches models, retrieval, memory, and tools. It classifies context locally, enforces versioned policies, and records decisions without storing prompt content.
Key features
- 01Local context classification and lineage
- 02Versioned policy preview and replay
- 03Sensitive-data routing restrictions
- 04Governed function and MCP tool calls
- 05Content-free audit evidence
- 06Usage limits and observability
Use cases
- 01Keep repository secrets on-device
- 02Require approval for risky tool calls
- 03Test policy changes in CI
- 04Audit decisions without prompt logs
MCP support
Yagami exposes a Streamable HTTP MCP interface and applies its shared policy, lineage, transformation, and audit pipeline to MCP calls. It can evaluate tool calls before execution and require one-time approvals.
Configuration
Local server config is the same for every client. Copy it into your client’s MCP config file.
uvx yagamiYAGAMI_HEADLESSYAGAMI_MCP_SERVER_ENABLEDYAGAMI_REQUIRE_AUTHSecretLocal servers need a runtime on your machine (e.g. Node.js 18+). Config file locations differ by client; see your client’s docs.
Tools
Local servers expose tools only once running on your machine, and the maintainer has not provided a tool list.
Details
From the project READMEYagami
Open-source AI context firewall for governed model, retrieval, memory, and tool access.



Documentation | Gateway API | Deployment | Security | Roadmap
Try it in 60 seconds
The no-credential demo uses your configured Ollama model when it is installed; otherwise it opens a clearly labeled policy-only fallback. Choose one command:
uvx yagami demo
# or: python -m pip install yagami && yagami demo
# or: docker run --rm -p 127.0.0.1:8000:8000 ghcr.io/matthewtracy/yagami:latest yagami demo --host 0.0.0.0 --allow-remote
Open http://127.0.0.1:8000, or use
docker compose -f compose.demo.yaml up from a clone. Demo mode blocks cloud
routing while exercising the UI, policy, lineage, storage, and audit path. For
local AI answers, install Ollama and run
ollama pull llama3.2:3b-instruct-q4_K_M before starting the demo.
https://github.com/user-attachments/assets/a7be9449-eafc-4acb-99b6-ea39edc43cd2
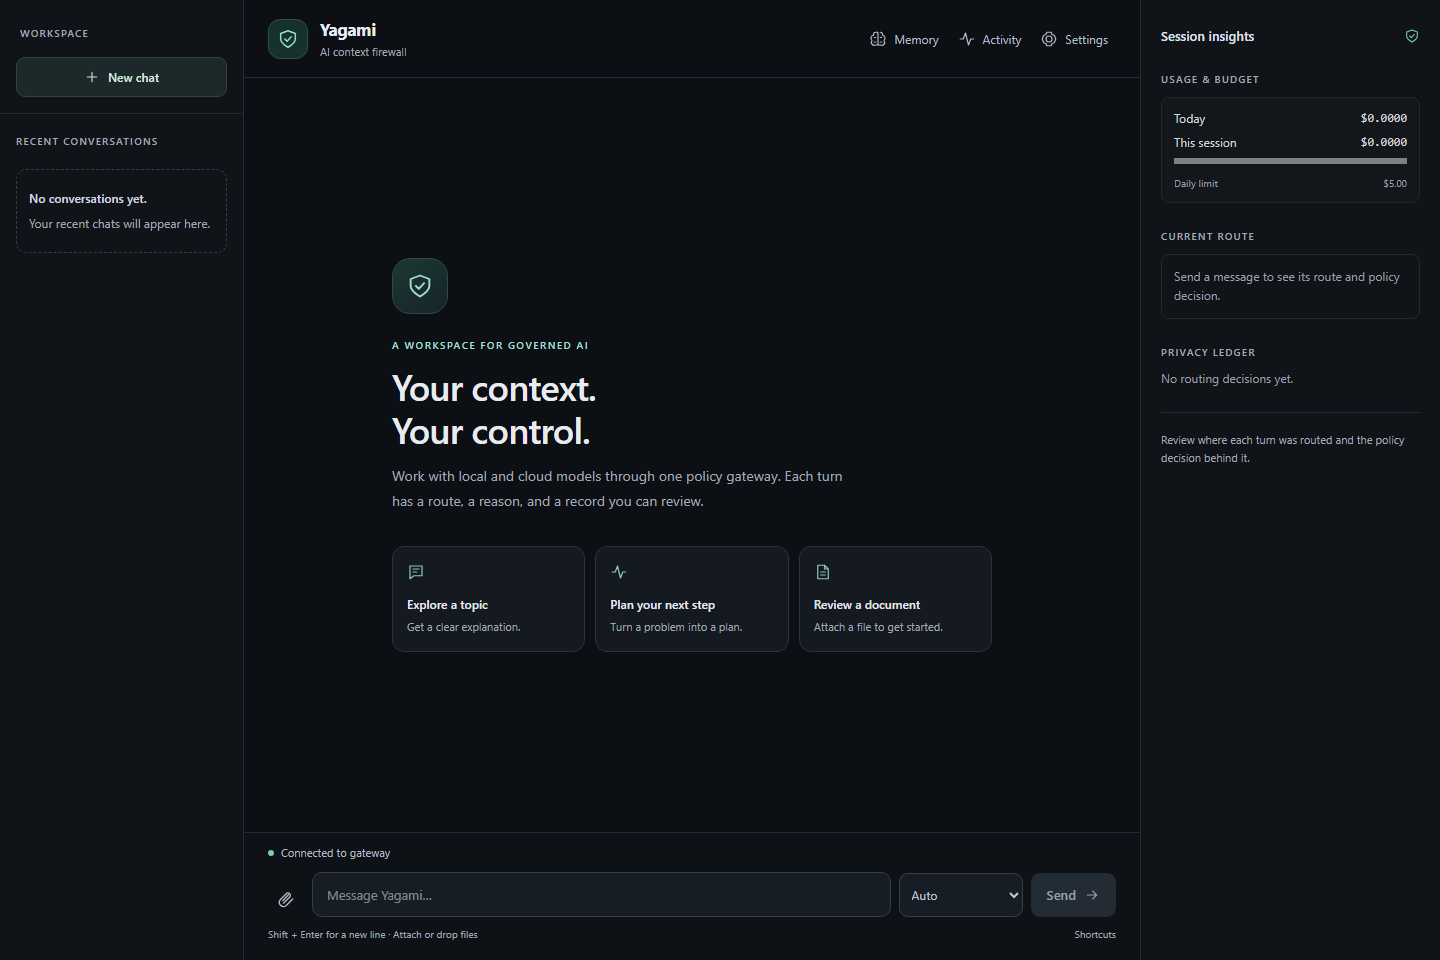
Yagami is for developers and platform/security teams that need to control where agent context goes and which tools it may execute. For example: a coding agent can keep repository secrets on-device and require an identity-bound, one-time approval before a dangerous tool call.
Yagami sits between software and local models, cloud LLMs, retrieval systems,
memory, and tools. Existing OpenAI SDK applications can adopt it by changing
one base_url; Yagami then classifies context locally, applies versioned
policy, and records content-free evidence for each decision.
Take the no-data security tour or run the flagship security demos for secret containment, poisoned retrieval, and identity-bound tool approval.
Protect an application
Initialize persistent user configuration, check the host, and start Yagami:
yagami init
yagami doctor
yagami serve
Install yagami[providers] when the Yagami process or the example client uses
Anthropic/OpenAI-compatible SDKs. PDF ingestion and OS key storage are separate
ingest and desktop extras; see configuration.
Then point an OpenAI client at the gateway:
from openai import OpenAI

client = OpenAI(
    base_url="http://127.0.0.1:8000/v1",
    api_key="your-yagami-project-key",
)

response = client.chat.completions.create(
    model="yagami-auto",
    messages=[{"role": "user", "content": "Summarize this document."}],
    metadata={
        "purpose": "internal-documentation",
        "sensitivity": "none",
        "session_id": "example-session",
    },
)
print(response.choices[0].message.content)
Supported caller sensitivity values are none, phi, phi_medical, and
secret. A caller hint can make the policy stricter; it cannot lower a
sensitivity detected by Yagami.
For production authentication, policy, and deployment settings, follow the deployment guide.
Why teams use Yagami
- Deterministic containment after classification. Once context is labeled as PHI or secret, default policy permits local backends only. Sensitive history and tool results inherit the same restriction.
- One governed data plane. Chat Completions, Responses, the browser chat, and MCP use the same policy, lineage, transformation, output-DLP, budget, and audit pipeline.
- Policy as code. Preview and replay decisions, run regression cases in CI, and promote deterministic Ed25519-signed policy bundles.
- Evidence without prompt logging. Policy passports, hash-chained audit records, Prometheus metrics, and OpenTelemetry spans carry labels, hashes, IDs, and counts rather than prompt or completion content.
- Model choice without policy duplication. Route to local engines, direct cloud providers, or an existing OpenAI-compatible gateway behind one enforcement point.
- Governed tools. Evaluate function tools and MCP calls before execution, require short-lived one-time approvals, and keep inbound credentials from being forwarded to downstream servers.
Core capabilities
| Area | Included |
|---|---|
| Compatible APIs | OpenAI Chat Completions, core Responses API, Streamable HTTP MCP |
| Identity | Scoped project API keys and OIDC/JWT workload identity |
| Policy | Versioned YAML/JSON rules, restrictive merging, preview, replay, shadow mode, regression tests, signed bundles |
| Privacy | Local classification, caller sensitivity, context lineage, AES-GCM tokenization, rehydration, output DLP, optional Presidio |
| Tools | Function calling, governed built-in skills, stdio and remote MCP, one-time approvals |
| Operations | Spend/rate/concurrency/context limits, health checks, Prometheus, OpenTelemetry, SIEM export, approval webhooks |
| Packaging | Python 3.11-3.14, PyPI, non-root container, Docker Compose, Helm, SBOMs, checksums, and build provenance |
Models and integrations
Local generation works with Ollama, llama.cpp through
the optional llama-cpp-python runtime, and Microsoft Foundry Local through
its loopback OpenAI-compatible service. Direct cloud adapters cover Anthropic,
OpenAI, Mistral, Groq, OpenRouter, Google Gemini, and Stability AI image
generation.
Yagami also works with LangChain/LangGraph, the Vercel AI SDK, Microsoft Presidio, Splunk HEC and generic SIEM webhooks, Slack and Teams approval notifications, and upstream gateways such as LiteLLM, Portkey, Kong, or Envoy. See the integration recipes.
How it compares
Yagami is not trying to replace every gateway, validator, or security scanner. Its focus is deterministic post-classification containment, governed tool execution, and content-free decision evidence. See the honest comparison guide for when LiteLLM, Guardrails AI, NeMo Guardrails, Presidio, LlamaFirewall, or a direct provider SDK is the better choice—and how to combine them with Yagami.
How enforcement works
flowchart LR
    A["Application or agent"] --> B["Authentication and project limits"]
    B --> C["Local classification and context lineage"]
    C --> D["Versioned policy"]
    D --> E{"Allowed destination or capability"}
    E --> F["Local or approved model"]
    E --> G["Retrieval, memory, or tool"]
    F --> H["Output inspection"]
    G --> H
    H --> I["Response"]
    D --> J["Content-free policy passport and audit chain"]
    H --> J
Policy is the final authority. Slash commands and explicit backend selection cannot override a sensitive-data restriction. Classifier failures fail local by default, and cloud routes can be blocked entirely or stopped at a daily spend cap.
Important limitations
Yagami is an enforcement component, not a compliance certification. Automated detection can miss sensitive data. Strict deployments should declare sensitivity at the caller, use a local-only policy, test organization-specific cases, encrypt storage at the host or volume layer, and review the threat model.
The project is alpha. Validate policy and failure behavior against your own requirements before production use.
Documentation
Contributing
Focused issues and pull requests are welcome. Read CONTRIBUTING.md, the security policy, and the code of conduct.
License
MIT - Copyright (c) 2026 Matthew Tracy and Yagami contributors.
Comments
New to MCP?
From what the protocol is to installing your first server, these answers cover most first questions.
An open protocol that defines how AI applications connect to external tools and data in a uniform way. Clients talk to the model; MCP servers provide tools, resources and prompt templates. They exchange standard messages, so one server can be reused by many clients.